Now you are being baited via WhatsApp!
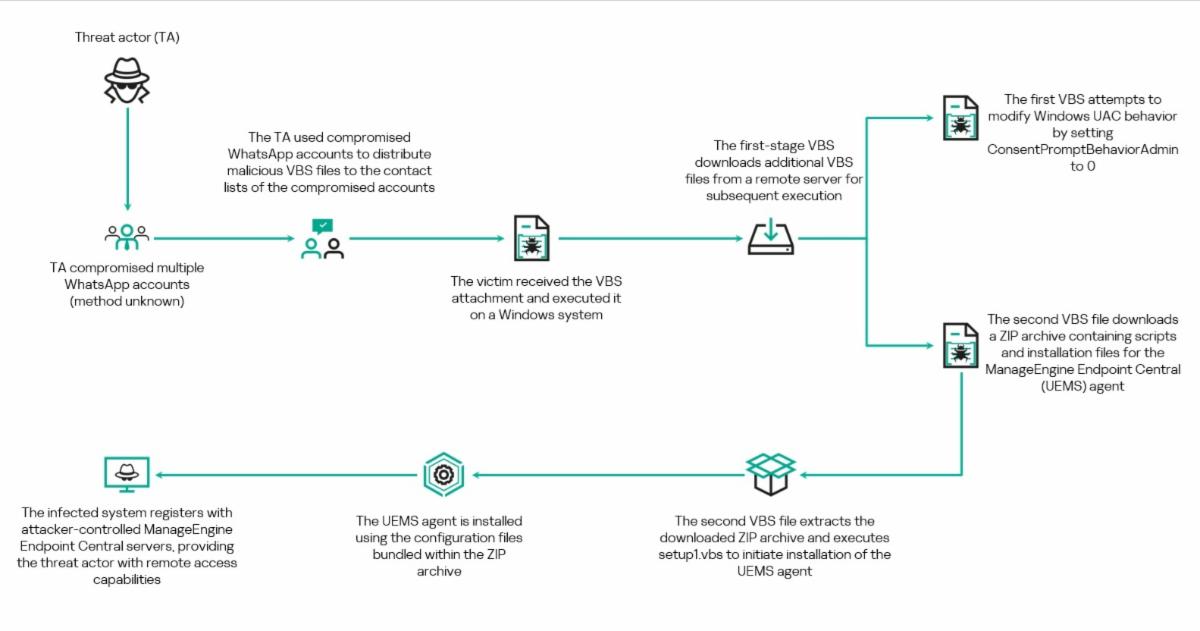
Attackers are compromising WhatsApp accounts and using them to send fake business and financial documents to the account owner’s contacts.
The files have convincing names such as Financial Reports, Account Statement or Outstanding Payment List.... and because they appear to come from somebody you know, curiosity and trust do the rest.
By doing homework on you and your colleagues, the bad guys can send a document that may appear relevant to your current work, so of course you will open it, right?
The attachment is actually a malicious VBScript file. The victim must first download it and then open it, and may even have to approve an administrator prompt.
Once the human being has kindly helped it through all those security barriers, it installs a legitimate ManageEngine remote-management tool, giving the attackers remote access to the computer.
The lesson is simple.... a familiar name and photograph in WhatsApp does NOT mean the message is safe.
Never open an unexpected attachment without independently checking with the sender, preferably by calling them.
Files ending in VBS, VBE, EXE, BAT, CMD, JS or PS1 should immediately set off alarm bells.
Technology can block a lot.... but it cannot always protect somebody who downloads the file, opens it and then clicks YES!
This is why security awareness training is no longer a nice-to-have annual tick-box exercise. Users need to be trained continuously, because the attacks are now continuous, personalised and increasingly AI-assisted. Please contact your First Technology Group account manager to get in touch with our training specialists, who can help you review the right security awareness and phishing simulation options for your organisation..
|